Warpgate is a smart & fully transparent SSH, HTTPS, Kubernetes, MySQL, PostgreSQL, RDP and VNC bastion host that doesn't require a client app or an SSH wrapper. Set it up in your DMZ, add user accounts and easily assign them to specific hosts and URLs within the network. Warpgate will record every session for you to view (live) and replay later through a built-in admin web UI. Browser-based SSH, RDP and VNC access…
Warpgate is a smart & fully transparent SSH, HTTPS, Kubernetes, MySQL, PostgreSQL, RDP and VNC bastion host that doesn’t require a client app or an SSH wrapper.
Set it up in your DMZ, add user accounts and easily assign them to specific hosts and URLs within the network.
Warpgate will record every session for you to view (live) and replay later through a built-in admin web UI.
Browser-based SSH, RDP and VNC access is built in; native clients continue to work.
Not a jump host - forwards connection straight to the target in a way that’s fully transparent to the client.
Native 2FA and SSO support (TOTP & OpenID Connect)
Built-in brute-force protection with IP blocking and user lockout
For warpgate.yaml file options, see the configuration schema.
Setup-generated config files include a yaml-language-server schema reference for editor completion and validation.
How is Warpgate different from a jump host / VPN / Teleport?
Warpgate
SSH jump host
VPN
Teleport
✅ Precise 1:1 assignment between users and services
(Usually) full access to the network behind the jump host
(Usually) full access to the network
✅ Precise 1:1 assignment between users and services
✅ No custom client needed
Jump host config needed
✅ No custom client needed
Custom client required
✅ 2FA out of the box
🟡 2FA possible with additional PAM plugins
🟡 Depends on the provider
✅ 2FA out of the box
✅ SSO out of the box
🟡 SSO possible with additional PAM plugins
🟡 Depends on the provider
Paid
✅ Command-level audit
🟡 Connection-level audit on the jump host, no secure audit on the target if root access is given
No secure audit on the target if root access is given
✅ Command-level audit
✅ Full session recording
No secure recording possible on the target if root access is given
No secure recording possible on the target if root access is given
✅ Full session recording
✅ Non-interactive connections
🟡 Non-interactive connections are possible if the clients supports jump hosts natively
✅ Non-interactive connections
Non-interactive connections require using an SSH client wrapper or running a tunnel
Warpgate is being actively used in enterprise settings.
What’s planned and being worked on next is tracked on the public roadmap.
How it works
Warpgate is a service that you deploy on the bastion/DMZ host, which will accept SSH, HTTPS, Kubernetes, MySQL, PostgreSQL, RDP and VNC connections and provide an (optional) web admin UI.
Run warpgate setup to interactively generate a config file, including port bindings. See Getting started for details.
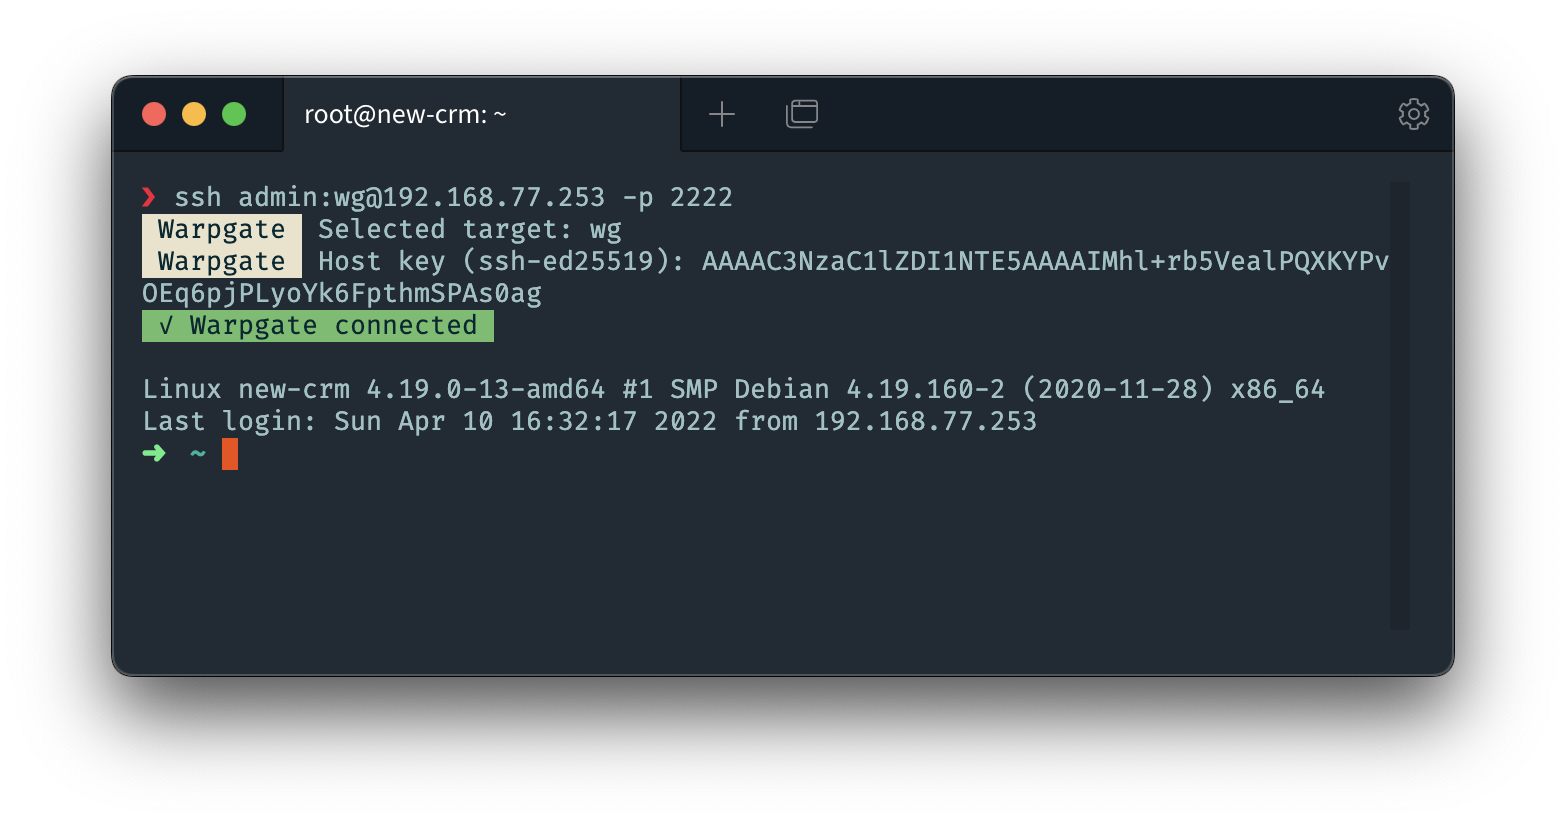
It receives connections with specifically formatted credentials, authenticates the user locally, connects to the target itself, and then connects both parties together while (optionally) recording the session.
When connecting through HTTPS, Warpgate presents a selection of available targets, and will then proxy all traffic in a session to the selected target. You can switch between targets at any time.
You manage the target and user lists and assign them to each other through the admin UI, and the session history is stored in an SQLite database (default: in /var/lib/warpgate).
You can also use the admin web interface to view the live session list, review session recordings, logs and more.
AI transparency disclosure
In late 2025, this project had started accepting AI-assisted contributions. Contributors are required to disclose AI use. I believe that by applying the same high quality standard to all PRs, whether AI-assisted or not, no sacrifice in quality or security needs to be made.
Since AI is a spectrum between braindead vibe bros and autocomplete users, I believe that being transparent about its use helps establish and limit the place of AI in this project.
Architectural and security decisions on this project are 100% human.
Contributing / building from source
You’ll need Rust, NodeJS and NPM
Clone the repo
Just is used to run tasks - install it: cargo install just
Warpgate admin and user facing APIs use autogenerated OpenAPI schemas and SDKs. To update the SDKs after changing the query/response structures, run just openapi-all.
Contributors ✨
Thanks goes to these wonderful people (emoji key):


评论