



Password4j is a Java user-friendly cryptographic library for encrypting and verifying passwords with different Key derivation functions (KDFs)
and Cryptographic hash functions (CHFs).
Algorithms can be configured programmatically or through a property file in your classpath see Configuration section.
The configurations are mostly dependent on your environment. Password4j delivers a tool that can create
a set of optimal parameters based on the system performance and the desired maximum computational time see Performance section.
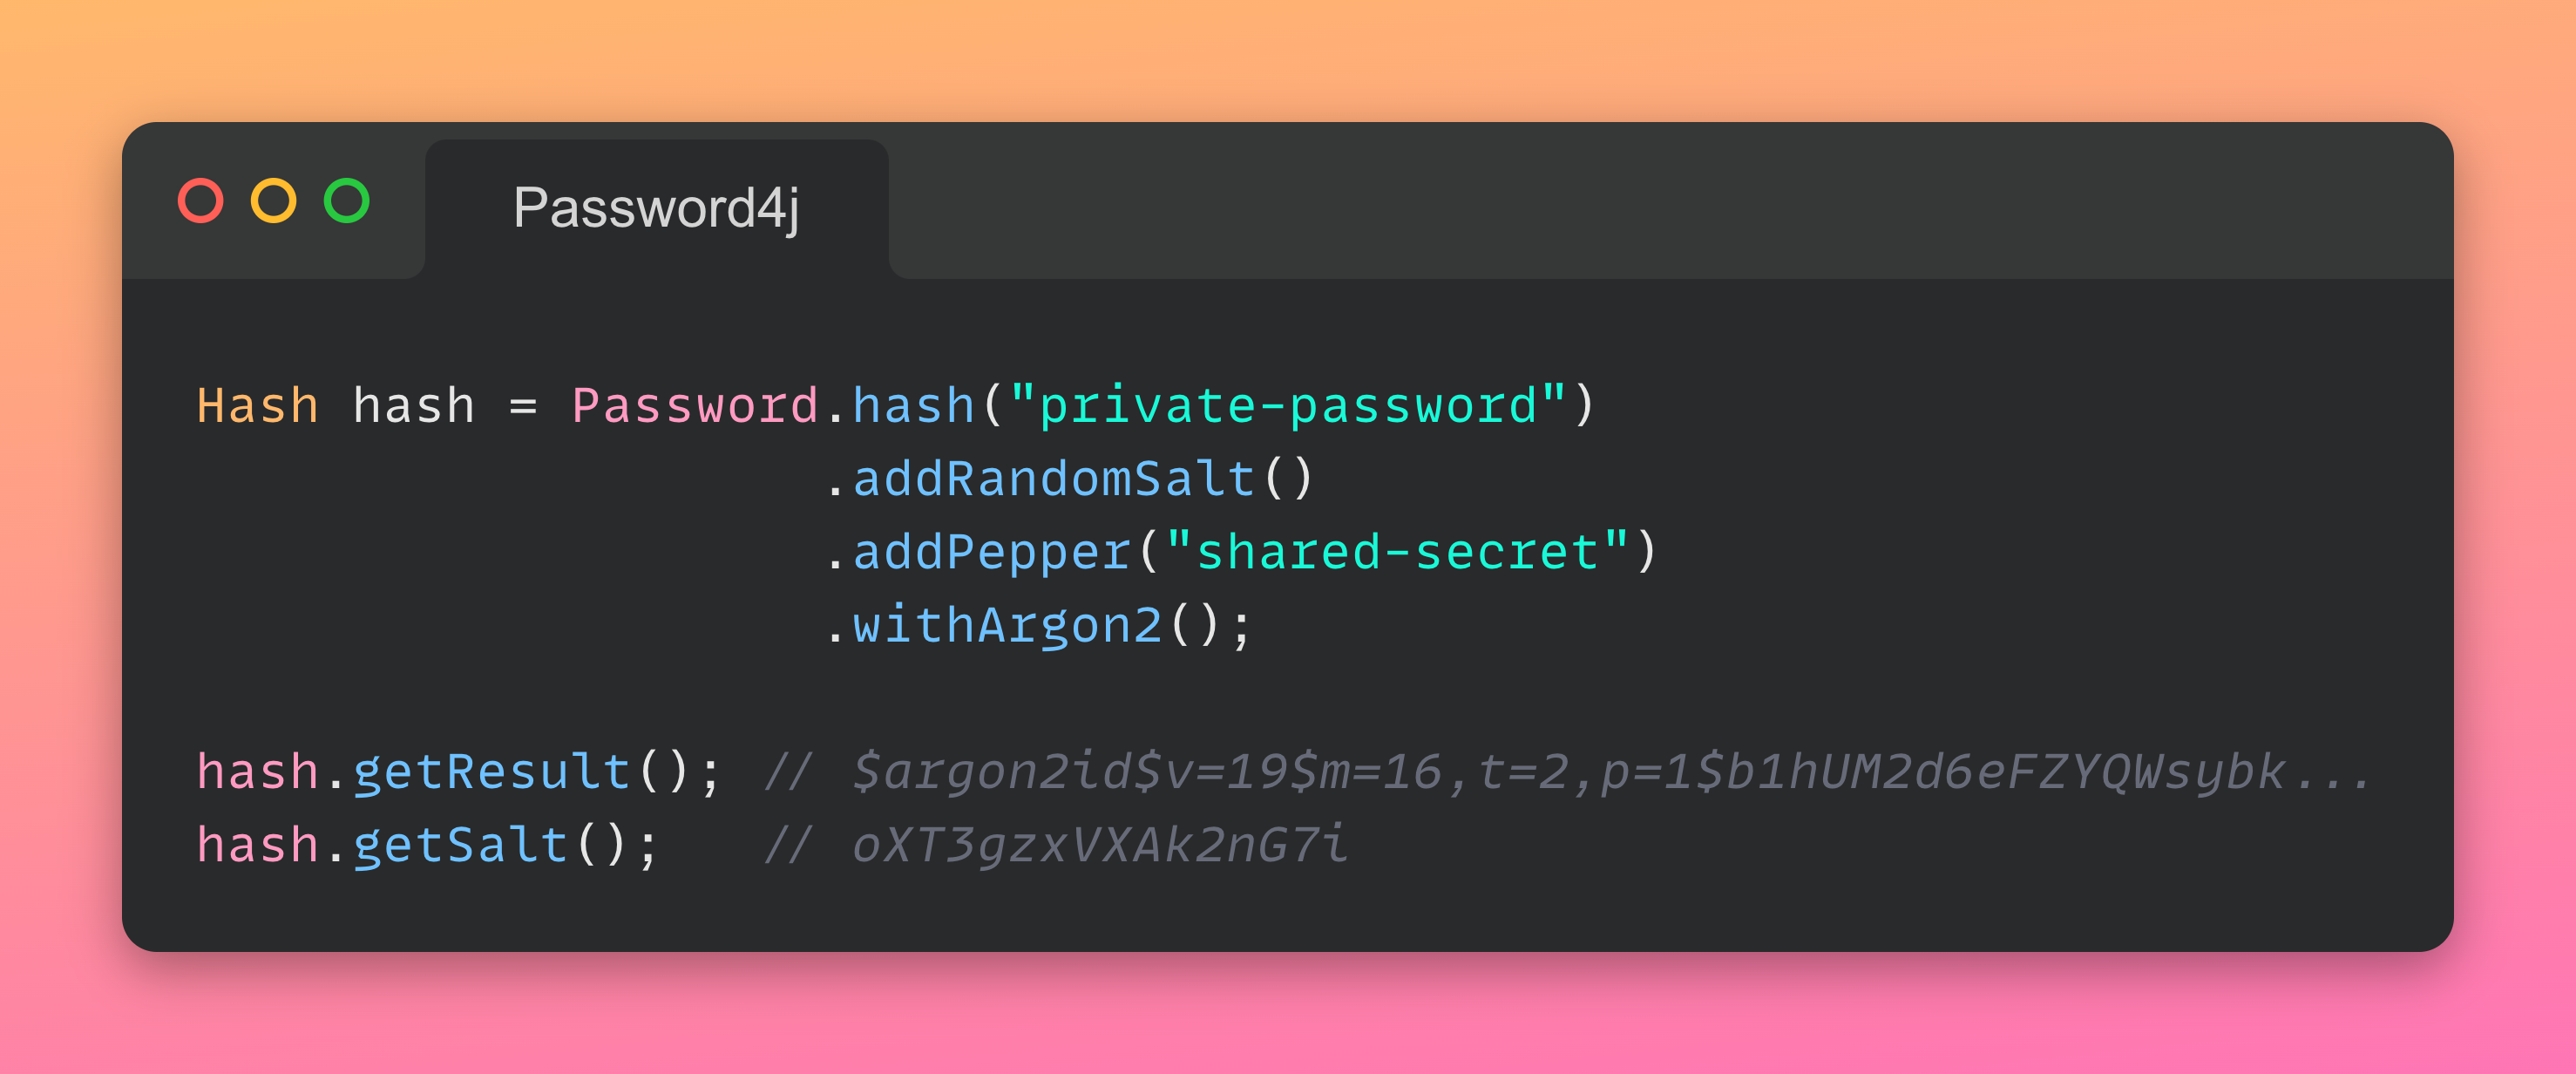
The library fully supports Argon2, bcrypt, scrypt, balloon hashing and PBKDF2
and can produce and handle cryptographic salt and pepper.
Documentation


The full documentation can be found here. For a quick start you can follow the instructions in the README.md.
The javadoc can be found here.
Installation
Password4j runs on Java 8 or higher versions by any vendor. It is compatible with Android API 21+ as well.
The artifacts are deployed to Maven Central.
Add the dependency of the latest version to your pom.xml:
<dependency>
    <groupId>com.password4j</groupId>
    <artifactId>password4j</artifactId>
    <version>1.8.4</version>
</dependency>
Usage
Password4j provides three main features: password hashing, hash checking and hash updating.
Hash the password
Here it is the easiest way to hash a password with a CHF (scrypt in this case). Salt and pepper may be optionally added to the builder:
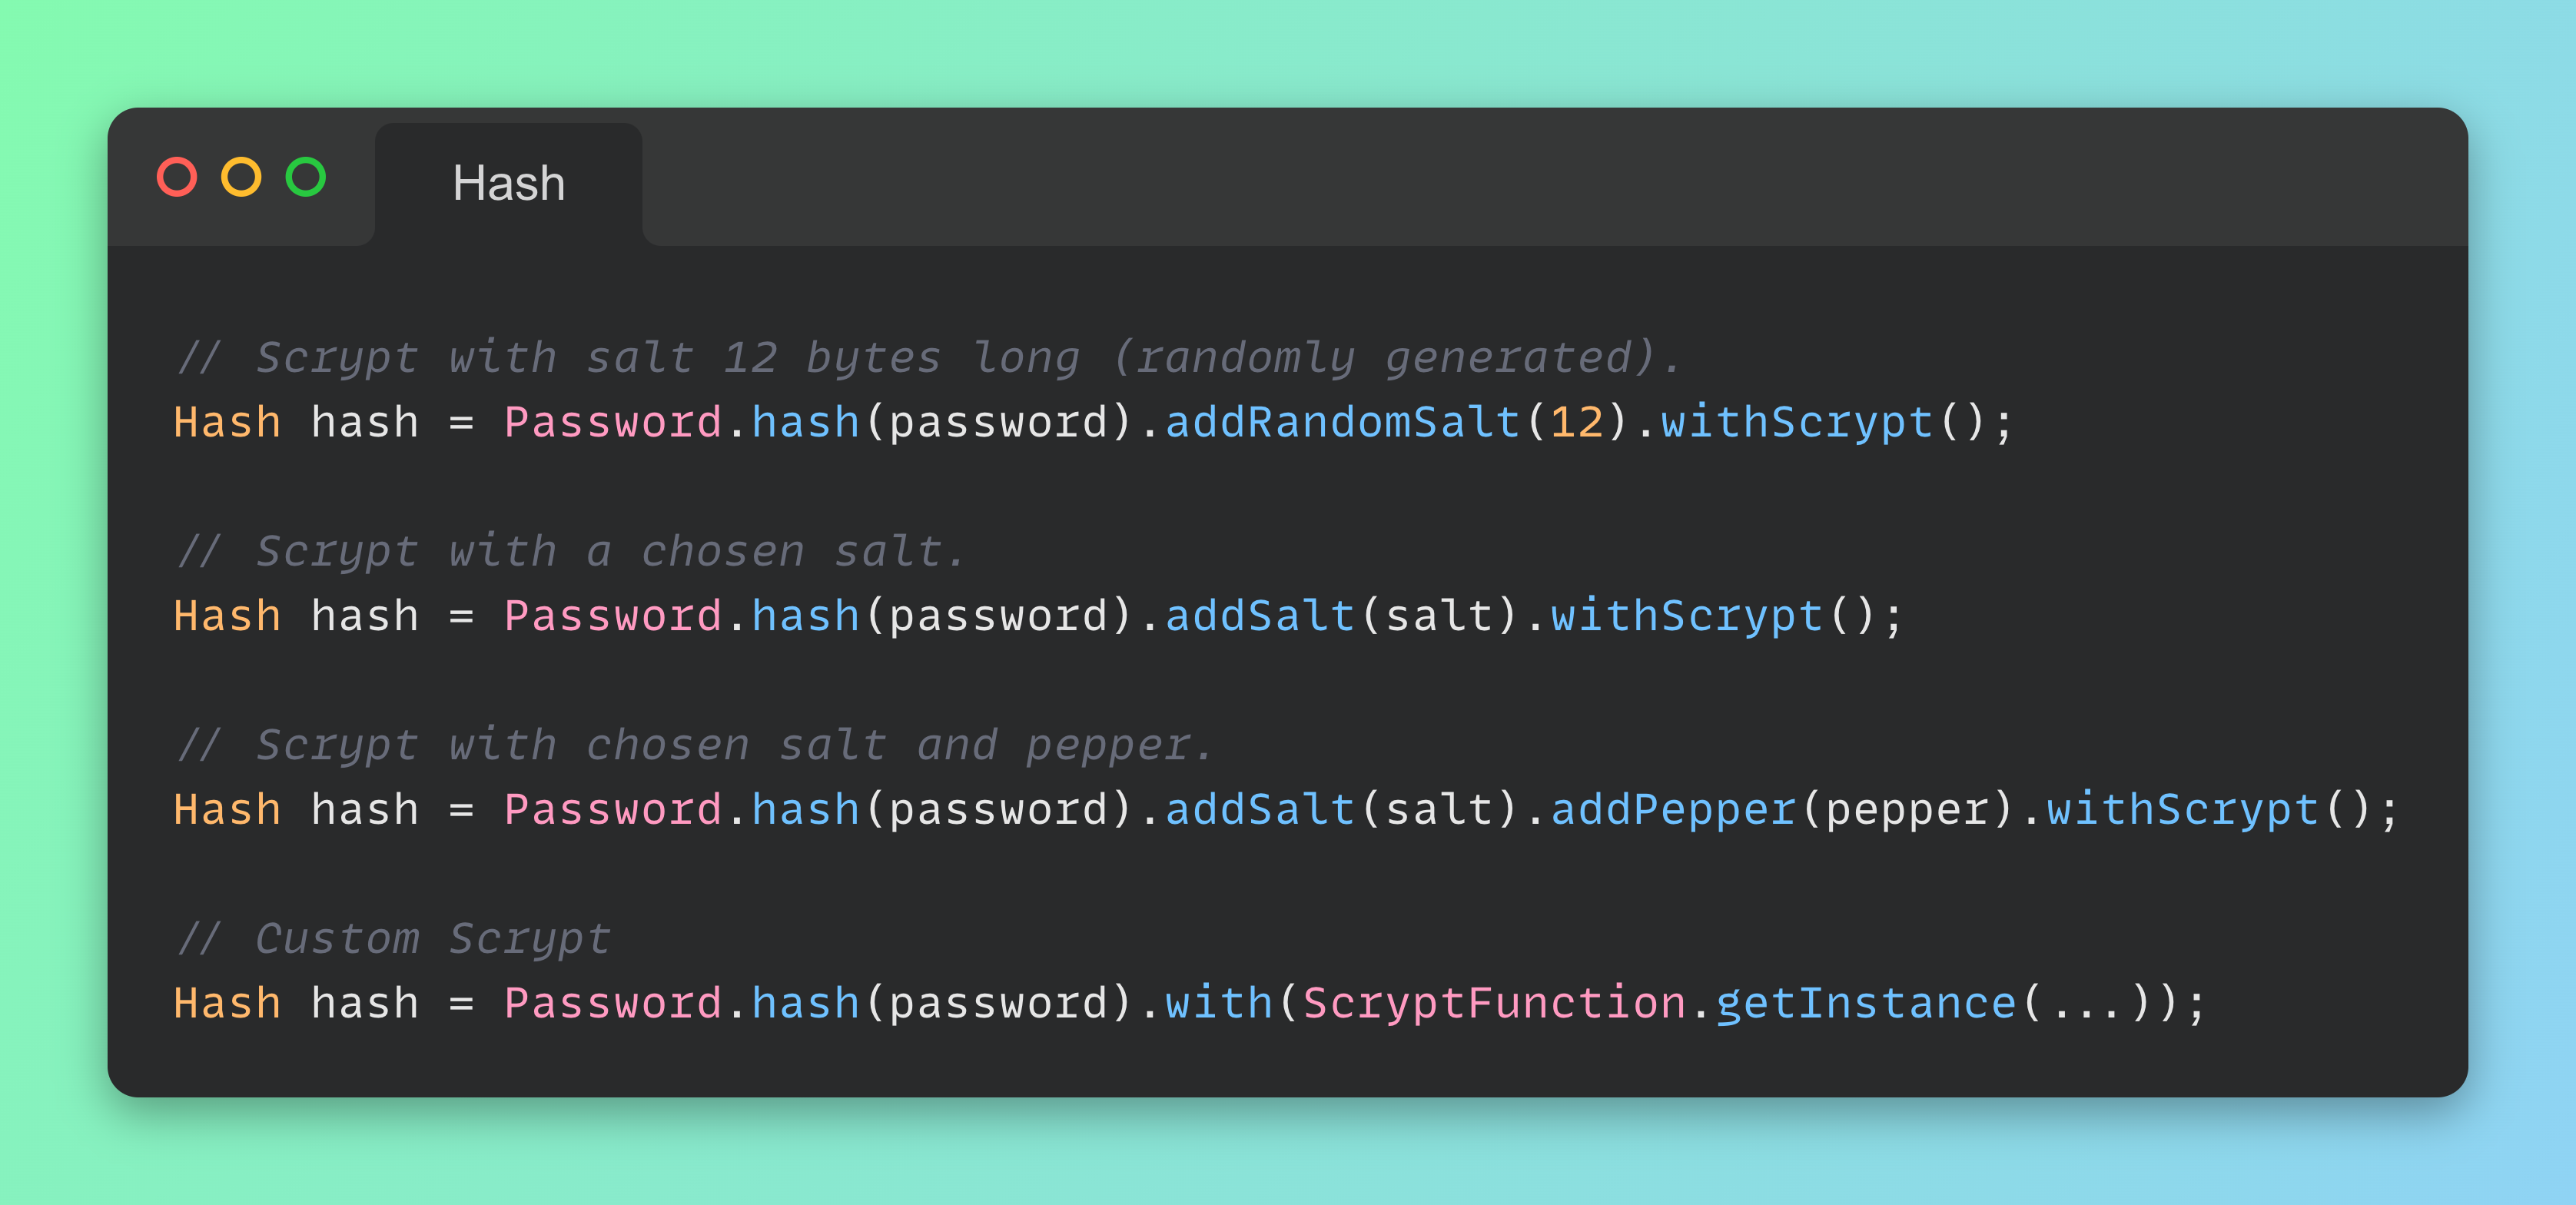
The same structure can be adopted for the other CHFs, not just for scrypt.
Verify the hash
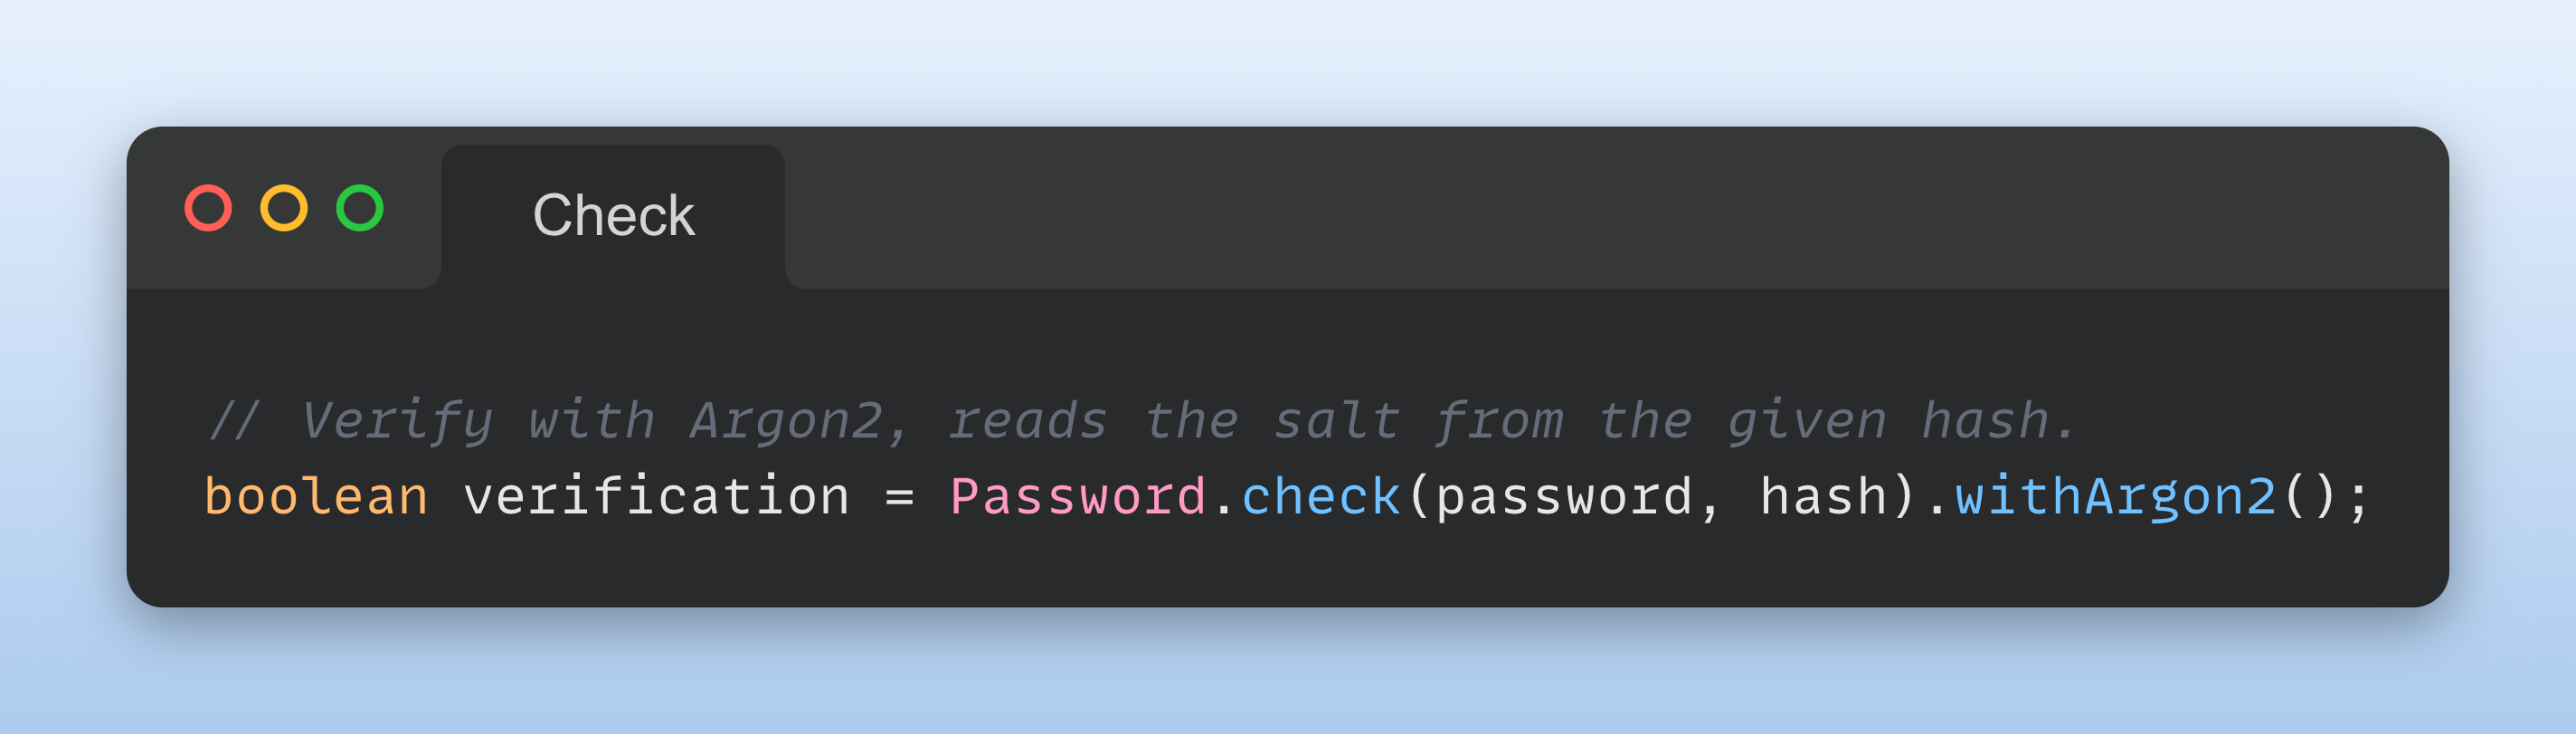
With the same ease you can verify the hash. Salt and pepper may be optionally added to the builder (Argon2 in this case):
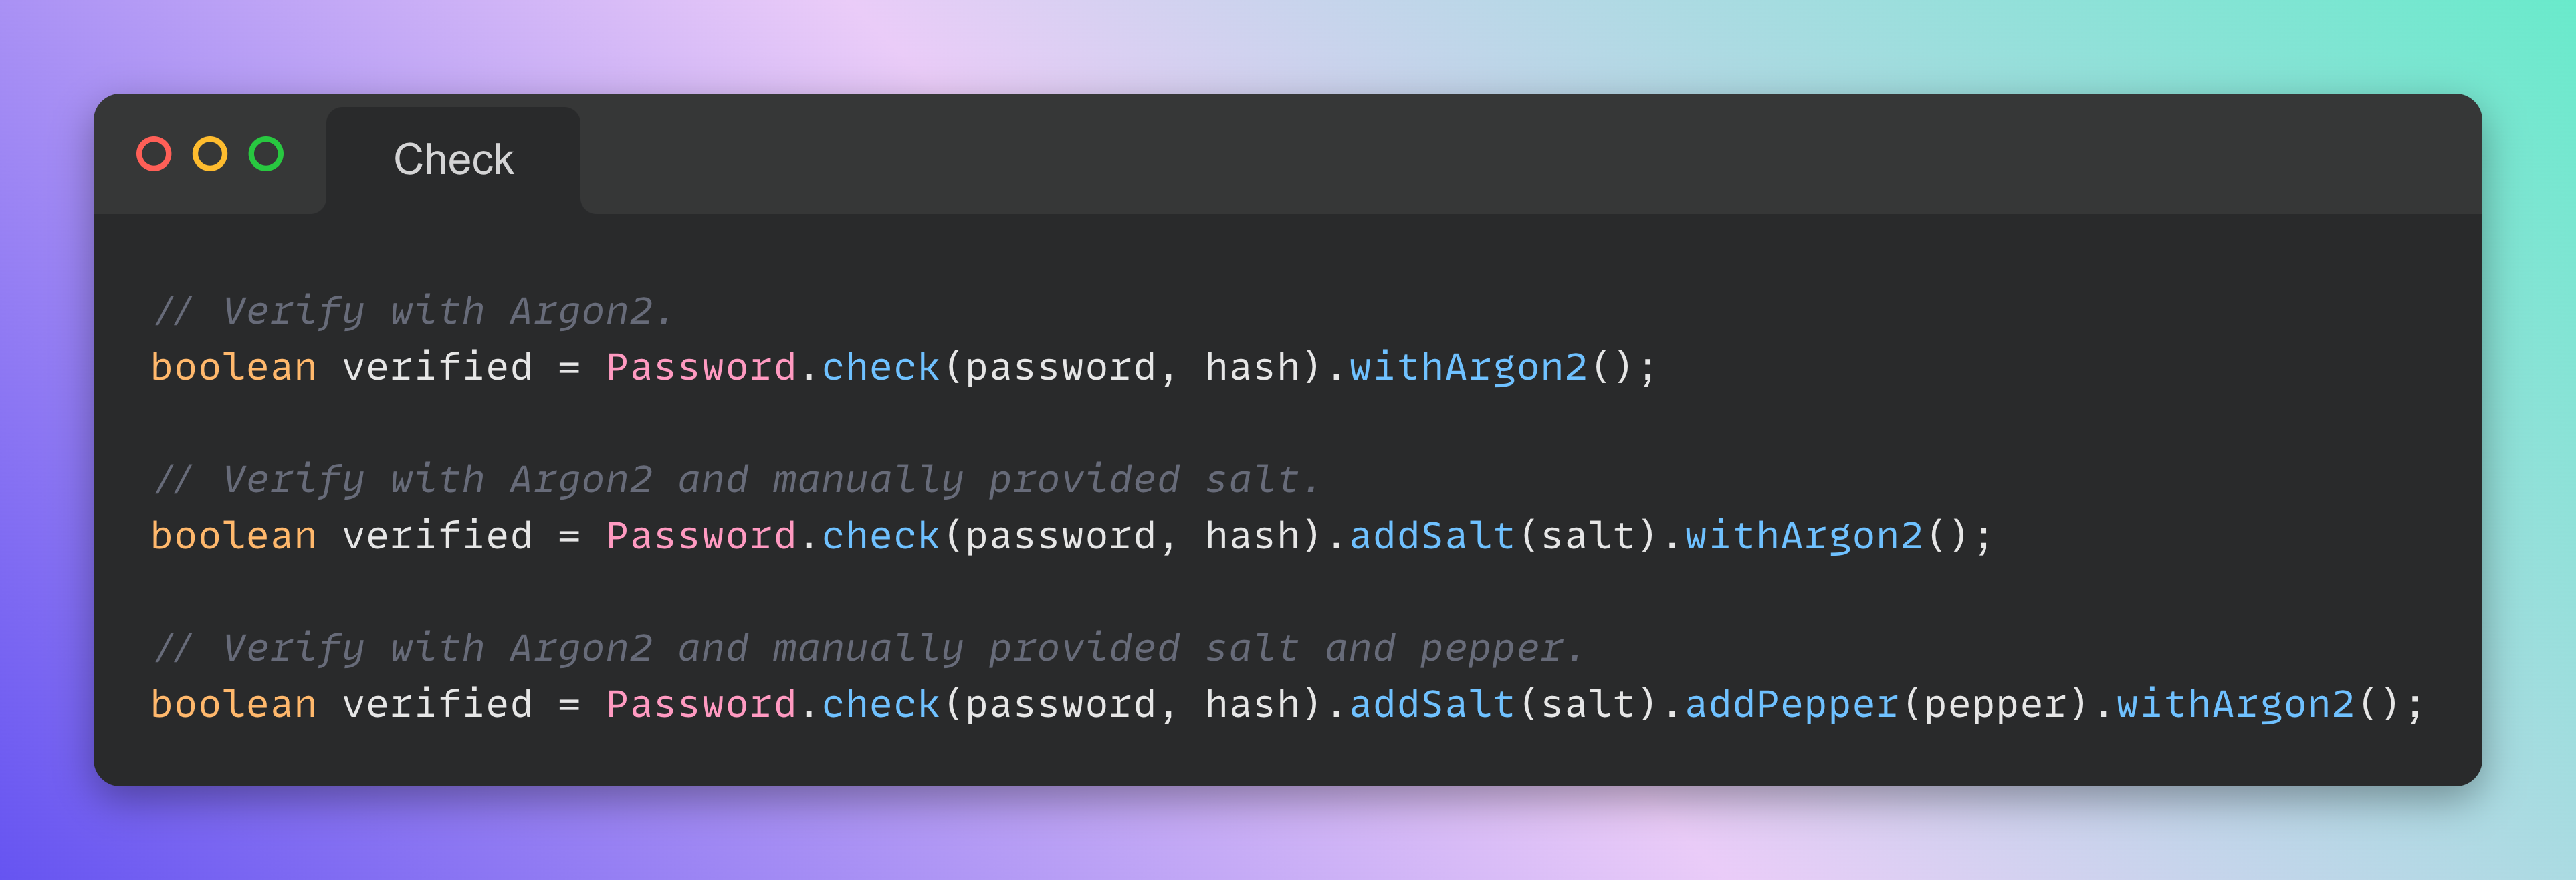
The same structure can be adopted for the other algorithms, not just for Argon2. Take in account that Argon2, bcrypt and scrypt store the salt
inside the hash, so the addSalt() method is not needed.
Update the hash
When a configuration is not considered anymore secure you can
refresh the hash with a more modern algorithm like this:
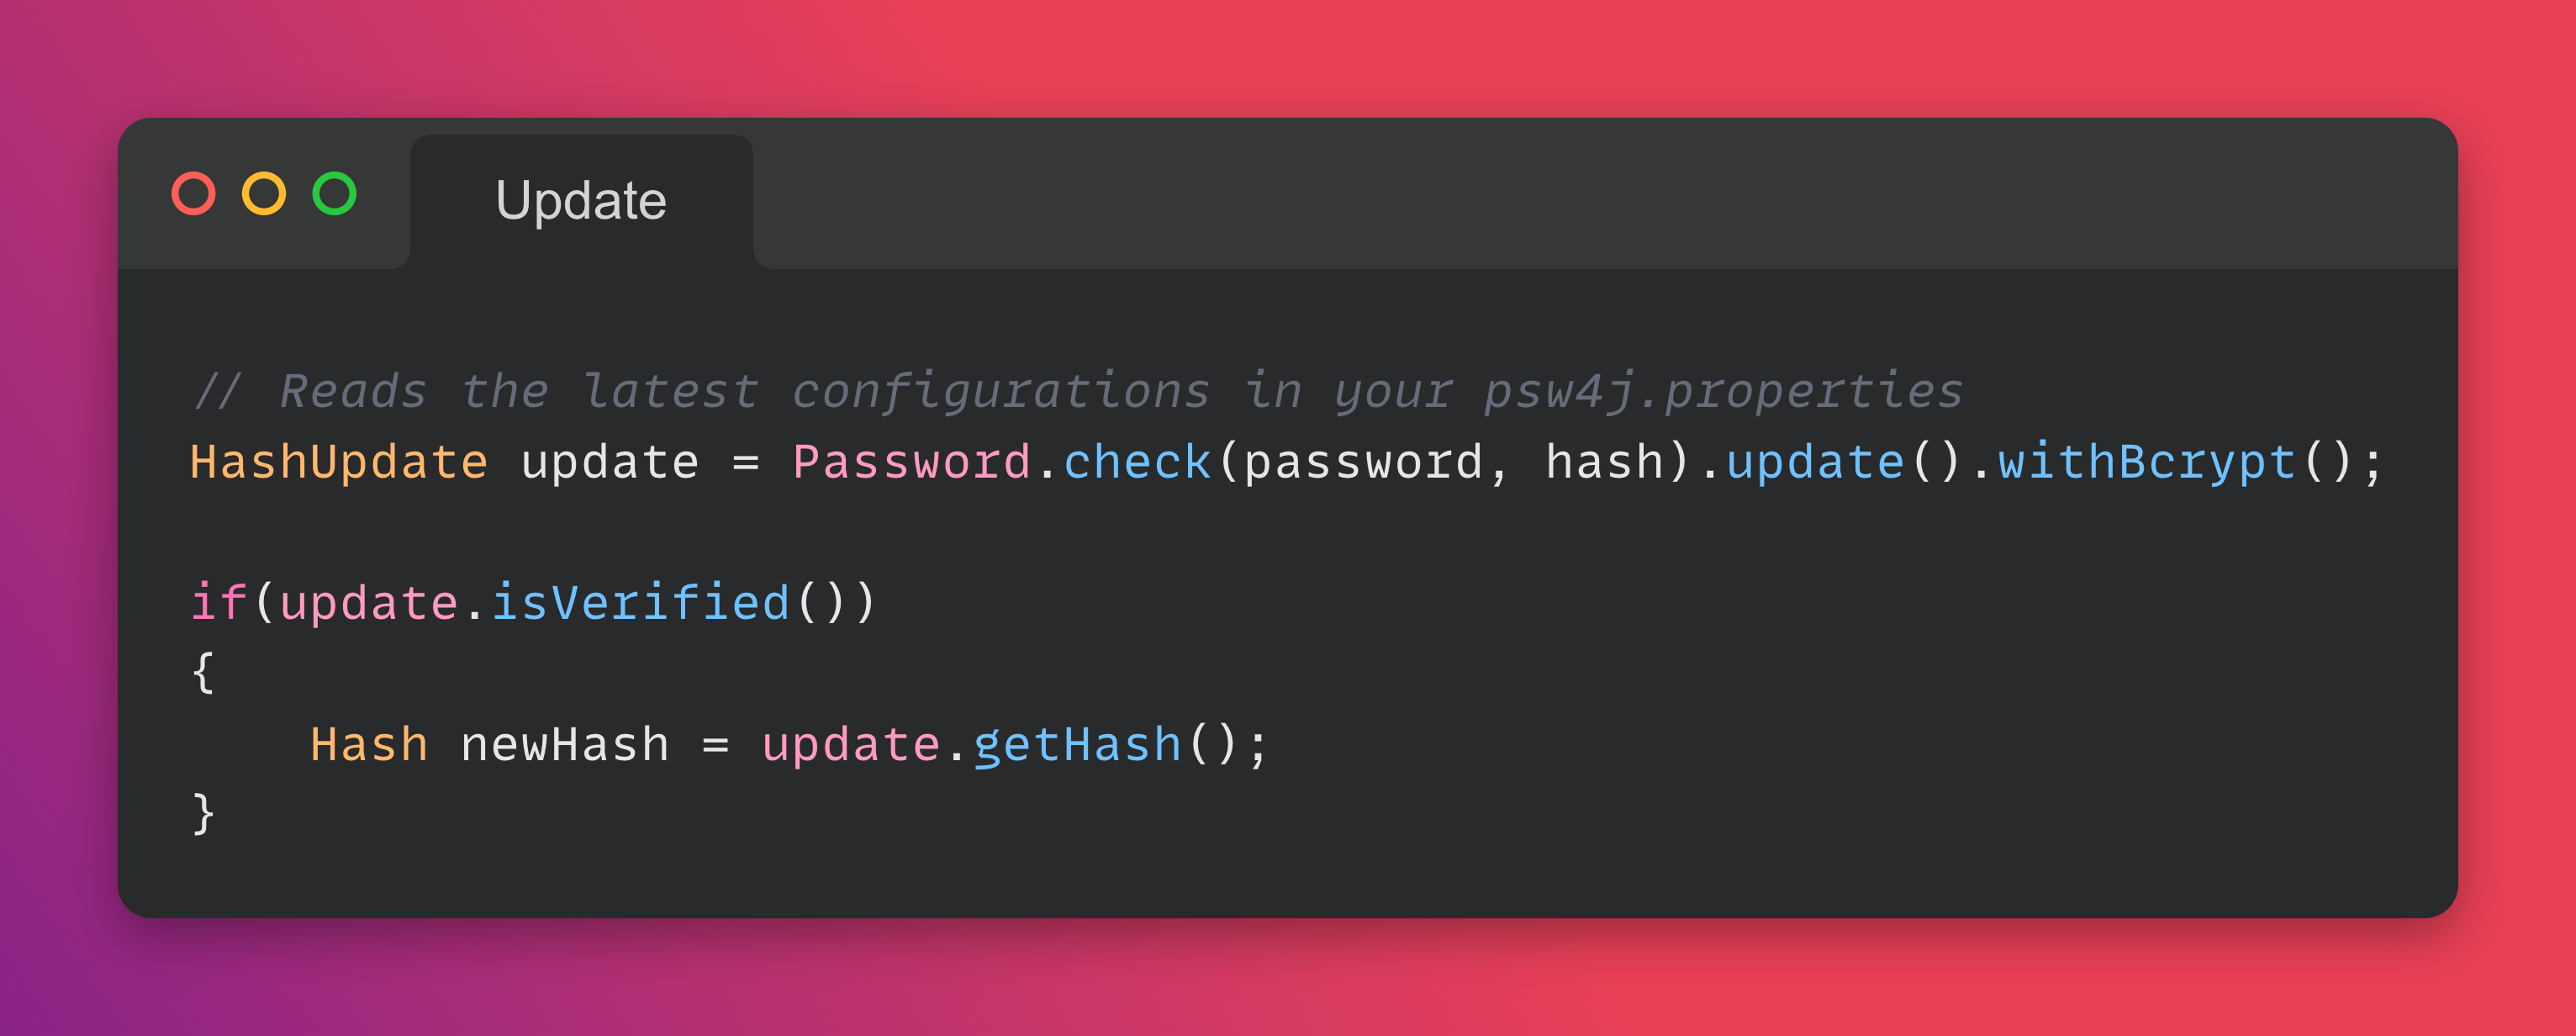
Or if you want to switch from a CHF to another one:

List of supported algorithms
| Key derivation Functions |
Since |
Notes |
| PBKDF2 |
1.0.0 |
Depending on the Security Services your JVM provides |
| bcrypt |
1.0.0 |
|
| scrypt |
1.0.0 |
|
| Argon2 |
1.5.0 |
|
| Balloon Hashing |
1.8.0 |
|
| Cryptographic Hash Functions |
Since |
Notes |
| MD Family |
1.4.0 |
|
| SHA1 Family |
1.4.0 |
|
| SHA2 Family |
1.4.0 |
|
| SHA3 Family |
1.4.0 |
Depending on the Security Providers your JVM provides |
Unsecure Algorithms
Many systems may still use unsecure algorithms for storing the passwords, like MD5 or SHA-256.
You can easily migrate to stronger algorithms with Password4j

Configuration
Password4j makes available a portable way to configure the library.
With the property file psw4j.properties put in your classpath, you can define the parameters of all the supported CHFs or just the CHF(s) you need.
Alternatively you can specify a custom path with the system property -Dpsw4j.configuration
java -Dpsw4j.configuration=/my/path/to/some.properties ...
Here’s a basic configuration (please do not use it in production, but instead start a benchmark session in your target environmentsee Performance section)
### Argon2
hash.argon2.memory=4096
hash.argon2.iterations=20
hash.argon2.length=128
hash.argon2.parallelism=4
hash.argon2.type=id


### bcrypt
hash.bcrypt.minor=b
# logarithmic cost (cost = 2^12)
hash.bcrypt.rounds=12


### scrypt
# N
hash.scrypt.workfactor=16384
# r
hash.scrypt.resources=16
# p
hash.scrypt.parallelization=1
# length
hash.scrypt.derivedKeyLength=64

### PBKDF2
# with HMAC-SHA256
hash.pbkdf2.algorithm=SHA256
# 64000 iterations
hash.pbkdf2.iterations=64000
# derived key of 256bit
hash.pbkdf2.length=256


### Legacy MessageDisgest
# algorithm
hash.md.algorithm=SHA-512
# append/prepend salt
hash.md.salt.option=append
Additionally you can define here your shared pepper
global.pepper=AlicePepper
and use it like this
// Hash
Password.hash("password").addPepper().withScrypt();

// Verify
Password.check("password", "hash").addPepper().withScrypt();
SecureRandom may be instantiated and used through SecureRandom.getInstanceStrong() to generate salts and peppers.
global.random.strong=true
but make sure that your JVM supports it and it points to a non-blocking source of entropy, otherwise you may experience huge performance dropssee SecureRandom.
This tool must be used in the target system because performances may vary on different environments.
Password4j is delivered with a tool that helps the developers to choose the right parameters for a specific CHF.
The class SystemChecker can be used to find these optimal values.
In the wiki you can find how to configure PBKDF2, bcrypt, scrypt and Argon2 depending on your responsiveness requirements.
JCA
Password4j is compatible with JCA. See this project for more details.
Contributing

Please read CONTRIBUTING.md for details on our code of conduct, and the process for submitting pull requests to us.
Versioning

We use SemVer for versioning.
For the versions available, see the releases on this repository.
Authors

- David Bertoldi - Main Maintainer - firaja
See also the list of contributors who participated in this project.
License

This project is licensed under the Apache License 2.0 License - see the LICENSE file for details
Changelog

See the CHANGELOG.md file for a more detailed description of each release.


评论